Open to opportunities

Nooh Ali Zidan
Offensive testing
for stronger defenses.

Information Security Analyst — AppSec & Vulnerability Research

HTB Certified Penetration Testing Specialist (CPTS) with hands-on experience in application security testing, vulnerability assessment, and secure code review. 60+ vulnerabilities responsibly disclosed through official bug bounty programs — now applying an offensive mindset to defensive security operations and AppSec assurance.
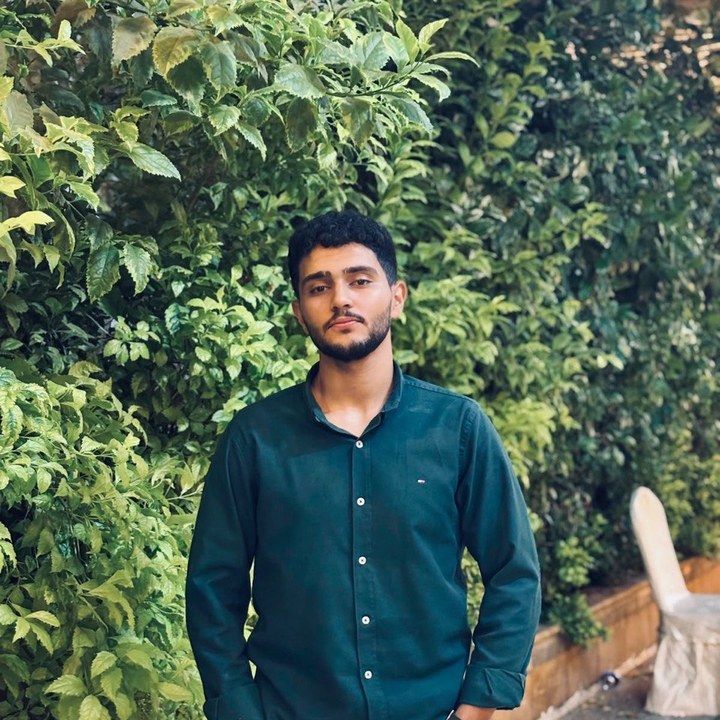
Nooh Ali Zidan
60+VULNS DISCLOSED
#46STANDOFF365 GLOBAL
61.9KSTANDOFF POINTS
10+YANDEX VERIFIED
// experience

Professional background

Bug Bounty Hunter — Standoff365 / YesWeHack

May 2025 – Present
  • Identified and responsibly disclosed 60+ valid vulnerabilities across multiple platforms, mapped to OWASP Top 10 categories.
  • Ranked 46th globally on Standoff365 with 61,900 points; earned Yandex Hall of Fame distinction for 10+ verified disclosures.
  • Authored reproducible vulnerability reports with severity ratings and remediation guidance for vendor security teams.

Security Intern — DEPI, Egyptian Ministry of Communications

Jun 2025 – Nov 2025
  • Completed intensive hands-on training in network defense, information security fundamentals, and threat analysis.
  • Practiced incident analysis, risk assessment, and secure system design through structured attack/defense simulations.

Core Member — Cybersecurity Track — IEEE Student Branch

Jan 2025 – Present
  • Led a cybersecurity workshop series reaching 50–100 attendees per event (3+ sessions delivered).
  • Organized security competitions and internal bug bounty practice sessions; mentored junior members.
  • Active Hack The Box contributor; member of IEEE Computer Society since 2023.
// projects

Engineering and security work

Source code for flagship projects is publicly available on GitHub.

Jan 2026 – Present

Spectrea Recon Framework

EASM platform · Go · FastAPI · PostgreSQL · React

Automated External Attack Surface Management platform orchestrating 26 modular scanners into a dependency-aware pipeline.

  • DNS/subdomain enumeration, port scanning, JS analysis, and secret/S3/JWT/container scanning with goroutine concurrency and a Redis-backed priority queue.
  • Local AI co-processors (FastAPI): secret validation with a fine-tuned NER model (StarPII) and graph-based lateral-movement attack-path generation (Flan-T5-Large).
  • Gin REST/WebSocket API, PostgreSQL and Redis persistence, React dashboard for live job monitoring, findings triage, and attack-path visualization.
GoGinRedis PostgreSQLFastAPINER WebSocketReact
View source — github.com/noohzidan/spectrea-recon-framework
Jul 2025 – Sep 2025

SPOTCHY

AppSec assessment · SAST + DAST · Secure code review

End-to-end security assessment combining static code review and dynamic exploitation across 18 vulnerability categories.

  • Covered SQL injection, XSS, CSRF, command injection, LFI, and more — with before/after remediation for every finding.
  • Produced developer-facing guidance on secure coding practices and a Secure SDLC policy draft.
  • Team of 2, Git branching with structured pull requests and peer review.
SASTDASTSecure SDLC Code ReviewGit
View source — github.com/noohzidan/SPOTCHY
Full repository archive on GitHub
// skills

Technical proficiency

Languages

GoPythonBash C++JavaScriptPHP C#

Security Testing

Burp SuiteOWASP ZAPMetasploit Nmapffufsqlmap NucleiSubfinderAmass Postman

Vulnerability Management

NessusAcunetixVulnerability Assessment SAST / DASTSecure Code Review

Core Concepts

OWASP Top 10Secure SDLC Penetration TestingExploit Development Privilege EscalationIncident Documentation Git & Version Control
// credentials

Certifications & recognition

Certifications

CPTS — HTB Certified Penetration Testing Specialist, Hack The Box 10-day practical exam: Active Directory, web & network pentesting, privilege escalation, commercial-grade reporting · verify
Sep 2026
Aug 2023
Coursework (no exam): CWES (HTB) · eWPTX · eWPT · Security+ · Network+
2023–2025

Verification links available on request — certificate credential IDs can be attached upon inquiry.

Awards & Recognition

Yandex Hall of Fame (2025) — view listing
Recognized for 10+ valid vulnerabilities reported via responsible disclosure.
Standoff365 — 46th globally
61,900 points earned through verified vulnerability discoveries.
60+ valid vulnerabilities disclosed
Across official bug bounty programs, mapped to OWASP Top 10.
IEEE Workshop Series
3+ sessions delivered, 50–100 attendees each, on security awareness and training.

B.Sc. Electronic Engineering — Faculty of Electronic Engineering, Menoufia University

2021 – 2026 · GPA 3.4
GPA 3.4

Let's talk security.

Open to AppSec roles, vulnerability assessment work, and security research collaborations. Always happy to responsibly discuss findings.